What Is a Hash Function? A Plain-English Guide
A hash function turns any input into a fixed-length fingerprint; here is how it works and why blockchains rely on it.
Quick answer
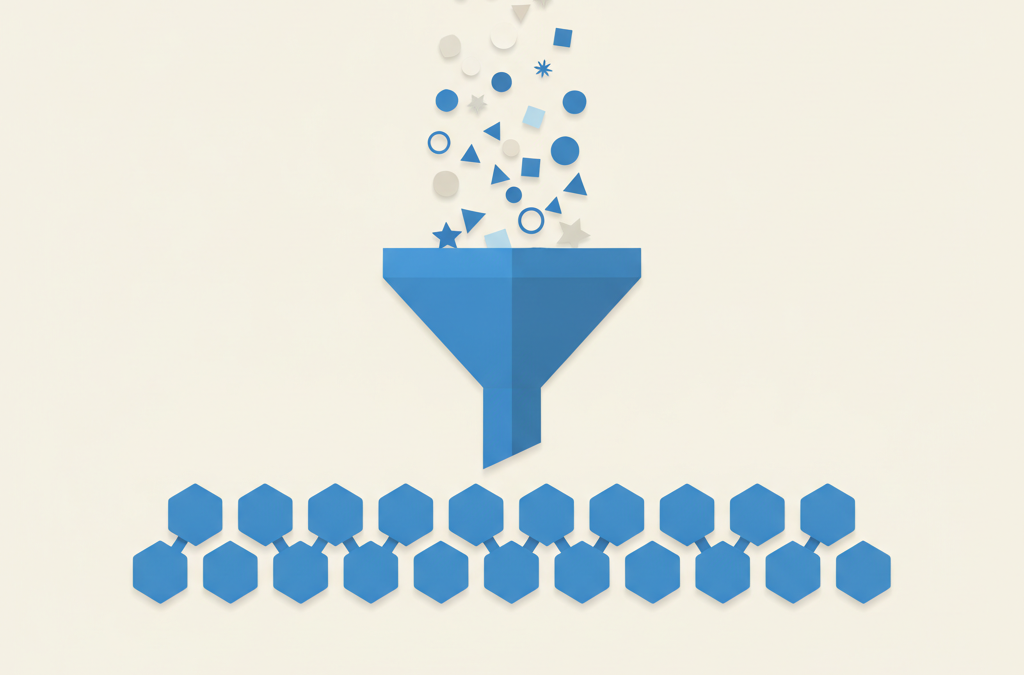
A hash function is a mathematical procedure that converts any input into a fixed-length string called a hash or digest. The same input always yields the same output, but changing the input even slightly produces a completely different result. Cryptographic hash functions such as SHA-256 are one-way and practically impossible to reverse, which is why blockchains use them to link blocks and verify data.
Key points
- A hash function maps an input of any size to a fixed-length output, often called a digest or fingerprint.
- Cryptographic hash functions are one-way: it is computationally infeasible to recover the input from the output.
- NIST specifies approved hash algorithms in FIPS 180-4 (the SHA-2 family, including SHA-256) and FIPS 202 (SHA-3).
- SHA-256 produces a 256-bit digest and is designed to offer roughly 128 bits of collision resistance.
- Hashing is not encryption: encryption is reversible with a key, while a cryptographic hash is intended to be irreversible.
- Bitcoin and other blockchains use hash functions to link blocks, form Merkle trees, and derive addresses.
A hash function is a mathematical procedure that takes an input of any size — a single word, a large file, or an entire blockchain transaction — and returns a fixed-length string of characters called a hash, digest, or fingerprint. The same input always produces the same output, yet changing the input even slightly produces a completely different result. In cryptography and in blockchains, this simple idea does an enormous amount of quiet work.
Hash functions are one of the foundational building blocks of modern computing. They power password storage, file-integrity checks, digital signatures, and the chains of linked blocks that give blockchains their name. Understanding what a hash function does — and, just as importantly, what it does not do — makes many crypto concepts far easier to follow.
What is a hash function in simple terms?
A hash function is like a machine that turns any document into a short, unique-looking code. Feed it the text of a novel and it returns a compact string; feed it a single letter and it returns a string of exactly the same length. That fixed-length output is the defining feature: no matter how large or small the input, the digest is always the same size.
Two properties make this useful. First, the process is deterministic — identical inputs always yield identical outputs, so anyone can recompute a hash and check it. Second, the output looks random and is extremely sensitive to change, so the fingerprint of one file is nothing like the fingerprint of a nearly identical file.
How does a hash function work?
Internally, a cryptographic hash function reads the input in fixed-size chunks and repeatedly mixes them through rounds of bitwise operations, additions, and rearrangements. The goal of this mixing is to spread the influence of every input bit across the entire output.
The result is the avalanche effect: flipping a single bit of the input changes roughly half of the output bits on average. This is why the hash of “hello” and the hash of “Hello” share no visible resemblance. The change is not proportional to the size of the edit; any change, however small, scrambles the whole digest.
Crucially, the process runs in one direction only. Computing a hash from an input is fast, but working backwards from a digest to recover the original input is designed to be practically impossible. That one-way quality is what separates a cryptographic hash from a simple checksum.
What makes a hash function "cryptographic"?
A cryptographic hash function must satisfy three security properties, as described in NIST guidance. Preimage resistance means that, given a hash value, it is infeasible to find any input that produces it. Second-preimage resistance means that, given one input, it is infeasible to find a different input with the same hash. Collision resistance means it is infeasible to find any two distinct inputs that hash to the same value.
NIST specifies approved algorithms in FIPS 180-4, which defines the SHA-2 family including SHA-256, and in FIPS 202, which defines SHA-3. As a rule of thumb, the preimage resistance of a well-designed function is close to its output size in bits, while its collision resistance is about half that. SHA-256 therefore produces a 256-bit digest and targets roughly 128 bits of collision resistance — a security level far beyond what brute force can reach.
Hash function vs encryption: what is the difference?
People often confuse hashing with encryption, but they solve different problems. Encryption is reversible and uses a key; hashing is one-way and uses no key. The table below summarizes the distinction.
| Property | Hash function | Encryption |
|---|---|---|
| Direction | One-way (irreversible) | Two-way (reversible) |
| Uses a key | No | Yes |
| Output size | Fixed length | Varies with input |
| Main goal | Integrity and verification | Confidentiality |
| Can recover input | No (by design) | Yes, with the key |
In short, encryption hides a message so the right person can read it later, while a hash produces a fingerprint that proves a message has not changed. The two are frequently combined — for example, a digital signature hashes a document first and then encrypts the digest with a private key.
Where are hash functions used in crypto?
Hash functions appear throughout cryptocurrency systems. Each block in a blockchain includes the hash of the previous block, so altering an old block would change its hash and break every link that follows — which is what makes the ledger tamper-evident. Bitcoin’s proof-of-work mining is essentially a race to find an input whose SHA-256 hash meets a difficulty target.
Hashing also builds Merkle trees, which let a network summarize many transactions in a single root hash and prove that one transaction belongs to a block without downloading all the others. Wallet addresses are commonly derived by hashing a public key, and message integrity checks rely on comparing digests. Beyond crypto, the same functions protect stored passwords and verify software downloads.
What are the limits and common misconceptions?
A hash is not encryption and does not keep data secret on its own; a digest of a short, predictable value can sometimes be reversed by simply hashing every likely input and comparing. This is why password systems add a random salt before hashing. A hash also does not compress data you can later restore — the original cannot be rebuilt from the digest.
Collisions are theoretically unavoidable because inputs are unlimited while outputs are finite, but for a secure function they are infeasible to find on purpose. Older functions such as MD5 and SHA-1 are considered broken for security use precisely because practical collisions were discovered, which is why current standards favor SHA-2 and SHA-3.
How do you choose a secure hash function?
For anything security-sensitive, the guidance is to stick with algorithms that have been publicly standardized and widely reviewed, rather than inventing a custom scheme. NIST-approved functions such as SHA-256, SHA-384, and the SHA-3 family have survived years of scrutiny by cryptographers around the world, which is a large part of why they are trusted.
The right output size depends on the job. Where collision resistance is the priority — for example, in digital signatures — a larger digest provides a wider safety margin, because collision strength is only about half the output length in bits. Where speed matters and only preimage resistance is needed, a 256-bit digest is typically more than sufficient. The key principle is to match the algorithm and its output length to the threat, and to retire functions as soon as the research community flags weaknesses, exactly as happened with MD5 and SHA-1.
It also helps to remember what a hash cannot do alone. On its own it does not authenticate a sender or keep a message secret; those goals require additional tools such as keyed message authentication codes or encryption layered on top. A hash is a component, not a complete security system.
The bottom line
A hash function is a fast, deterministic, one-way mapping from any input to a fixed-length fingerprint. Its value comes from being easy to compute, hard to reverse, and sensitive to the smallest change. Those qualities let blockchains link blocks, let networks verify data, and let systems check integrity without revealing the underlying content — making the humble hash one of the most important tools in all of cryptography.
Sources
Frequently asked questions
Is a hash function the same as encryption?
No. Encryption is a two-way process that scrambles data so it can be recovered later with a key, while a cryptographic hash function is a one-way process with no key and no intended way back to the original input. Hashing verifies integrity; encryption protects confidentiality.
Can two different inputs produce the same hash?
In theory yes, because a fixed-length output has finitely many possible values while inputs are unlimited. This is called a collision. A secure hash function is designed so that finding any collision is computationally infeasible in practice.
What is SHA-256 used for?
SHA-256 is a member of the SHA-2 family standardized by NIST in FIPS 180-4. It produces a 256-bit digest and is widely used in Bitcoin mining, digital signatures, certificate systems, and file-integrity checks.
Why do small changes make a completely different hash?
Well-designed hash functions exhibit the avalanche effect: flipping a single bit of input changes about half the output bits on average. This makes it easy to detect tampering, because any edit produces an obviously different digest.
Are hash functions safe against quantum computers?
There are no known classical preimage attacks on SHA-2 faster than brute force. Quantum search algorithms could weaken preimage resistance somewhat, so using longer digests such as SHA-256 or SHA-384 provides a large security margin.
Related
What Is a Nonce in Blockchain?
A nonce is a number used once: in mining it is the value miners change to find a valid block…
Token approvals and why they drain wallets
Token approvals explained: how the permissions you sign let contracts move your tokens, why unlimited approvals drain wallets, and how…
What gas fees actually pay for
Gas fees pay for the computation your transaction needs and ration limited block space. Here is what they actually fund…